
Overview
This Course is Skillsfuture funded (Up to 90%)
In today’s interconnected world, Operational Technology (OT) systems are critical to industries like manufacturing, energy, utilities, and transportation. However, the growing threat landscape demands that OT professionals not only understand how their systems function but also how to safeguard them from ever-evolving cyber threats.
ICS CYBERSECURITY FOUNDATION TRAINING COURSE has been specifically developed to empower industrial personnel with the most essential IT and OT security principles. Completing this series allows the trainee to be cyber aware in their daily job, knowing their risk on the job.
This DEFENDER FOR OT CYBERSECURITY COURSE is designed for technical professionals who need to deepen their expertise in securing OT systems. With a focus on attack methodologies, risk analysis, and security protocols, this course provides the tools and knowledge to stay ahead of the increasingly complex threats targeting OT environments. Using the MITRE ATT&CK Framework, participants will explore cutting-edge attack techniques and methodologies specifically for ICS, equipping them to identify vulnerabilities and respond proactively. The course also dives into risk analysis, security architecture, and lifecycle management, providing a holistic approach to OT cybersecurity. Through in-depth technical training and real-world applications, you will master the core concepts and advanced strategies required to protect OT systems against evolving threats.
WHY CHOOSE THIS COURSE?
Technical Focus: This course offers a technical and practical approach to OT cybersecurity, perfect for professionals already familiar with OT systems.
Designed for the Security Practitioner: Comprehensive understanding of attack methodologies, risk management techniques, and security protocols essential for defending OT environments
Expert-Led Training: Learn from instructors with deep experience in securing critical OT systems and mitigating sophisticated threats.
Elevate your cybersecurity expertise and develop the technical skills necessary to safeguard OT infrastructure from modern threats.
Enroll today to be part of a group of leading cybersecurity practitioners in securing the future of critical OT systems.
COURSE DURATION:
3 days of Instructor-led training
EXPECTATION AFTER THE TRAINING:
Participants will gain a foundational understanding of networking structures, including OSI and TCP/IP models, through a live analysis of TCP communication, examining each layer in detail.
Participants will explore the cyber kill chain from a MITRE perspective, gaining insights into adversarial tactics and strategies, enabling them to effectively defend against threats posed by nation-state actors and malicious hackers.
Participants will develop a comprehensive understanding of fundamental OT protocols, including an in-depth review of protocols such as Modbus.
Participants will analyze the mechanics of cyberattacks within an OT environment, assessing their potential impact on industrial plant operations.
Course Description & Learning Outcomes
WHAT WILL BE COVERED IN THE COURSE:
The ISA and the International Electrotechnical Commission (IEC) have collaborated to establish a set of standards known as the ISA/IEC 62443 series. This comprehensive course delves into the fundamental principles of these standards. These standards play a crucial role in the automation of industrial production processes, widely utilized in sectors such as power, water, oil, and natural gas. The ISA/IEC 62443 standards offer guidelines for optimal practices in industrial network security, with new technical specifications being evaluated every three years for potential adoption as new standards.
The following will be covered in the course:
This course takes a highly technical approach, immersing participants in hands-on exercises designed to simulate real-world cybersecurity scenarios within an OT environment. Attendees will engage in practical activities such as conducting basic reconnaissance attacks to identify vulnerabilities and mapping OT components within a network. These exercises are structured to provide participants with a deeper understanding of an attacker's mindset, enabling them to analyze potential threats and reinforce their defensive strategies effectively. These hands on technical exercise includes:
In-Depth Analysis of Endpoint Communication: Participants will conduct a detailed examination of network communication between two endpoints, breaking down packet-level interactions to understand how data is transmitted, received, and interpreted within an OT environment. This exercise will enhance their ability to detect anomalies and identify potential security threats within network traffic.
Comprehensive Breakdown of OT Protocols: Participants will analyze and dissect key OT protocols, such as Modbus, DNP3, and OPC UA, to gain a deeper understanding of their structure, functionality, and security implications. This knowledge will enable participants to assess vulnerabilities within these protocols and implement effective safeguards.
Live Attack Traffic Analysis Simulation: Through hands-on exercises, participants will simulate and analyze real-world attack traffic within a controlled environment. They will learn to identify malicious patterns, interpret logs, and apply cybersecurity tools to detect and mitigate threats effectively.
Simulation of a Cyberattack on an OT Environment: Participants will engage in a simulated cyberattack scenario within an OT setting, observing the attack lifecycle from initial infiltration to exploitation. This exercise will provide practical insights into adversarial tactics and techniques while reinforcing incident response strategies and defense mechanisms.
Understanding and Defending Against Passive vs. Active Threats: Participants will explore the distinctions between passive and active threats, analyzing their impact on OT systems. They will learn proactive defense strategies to mitigate passive threats, such as reconnaissance and eavesdropping, as well as countermeasures to defend against active threats, including system intrusions and sabotage. This segment will focus on implementing robust security controls to fortify OT environments against evolving cyber threats. To maximize the learning experience, participants are required to bring their own laptops, which will be used to interact with live attack simulations and defense technologies. Through guided practice, attendees will develop practical skills in both offensive and defensive cybersecurity methodologies, enhancing their ability to secure OT environments. Additionally, the course will provide an in-depth exploration of MITRE ATT&CK for Industrial Control Systems (ICS)—a comprehensive knowledge base that documents adversary tactics, techniques, and procedures (TTPs) specific to industrial environments. Participants will examine the various phases of an attack lifecycle, gaining insight into how cyber adversaries target critical assets and systems. Originating from MITRE's extensive research, this framework applies the ATT&CK methodology to ICS environments, offering a structured approach to understanding and mitigating threats in operational technology settings.
Learning Objective
By the end of the course, participants will be able to:
Apply technical and practical OT cybersecurity concepts to analyse and address security challenges in Operational Technology (OT) environments.
Understand and assess attack methodologies targeting OT systems, using recognised frameworks such as the Adversarial Tactics, Techniques, and Common Knowledge (MITRE ATT&CK) framework for Industrial Control Systems (ICS).
Apply risk management techniques and security protocols to strengthen the protection of OT infrastructure and industrial environments.
Evaluate security risks and defensive strategies to improve the resilience of critical OT systems against evolving cyber threats.
Recommended Prerequisites
Entry requirements
GCE ‘O’ Level qualification or equivalent
Proficiency in English
Basic IT knowledge
Basic cybersecurity knowledge
Pre-course instructions
This will be a hands on course and participants are expected to bring their own laptops
Schedule
End Date: 30 Apr 2027, Friday
Class dates are planned based on demand.
Location: Singapore University of Technology and Design (SUTD) - 8 Somapah Rd, Singapore 487372, 487372Agenda
| Day/Time | Agenda Activity/Description |
|---|---|
| Day 1 | Introduction to Information Technology (IT) and Operational Technology (OT) Environments Cybersecurity Management System (CSMS) – Deep Dive into Defensive Technologies Networking Basics for Industrial Environments – Lab Session Introduction to the MITRE ATT&CK Framework for Industrial Control Systems (ICS) |
| Day 2 | MITRE ATT&CK Lab 1 – Reconnaissance Techniques MITRE ATT&CK Lab 2 – Lateral Movement in OT Environments MITRE ATT&CK Lab 3 – Weaponisation Techniques MITRE ATT&CK Lab 4 – Command and Control (C2) |
| Day 3 | Understanding Modbus Protocols in Industrial Systems How Modbus Protocols Can Be Exploited in Cyber Attacks Overview of Open Platform Communications Unified Architecture (OPC UA) Protocol Security Risks and Attack Scenarios Involving Industrial Protocols |
Pricing
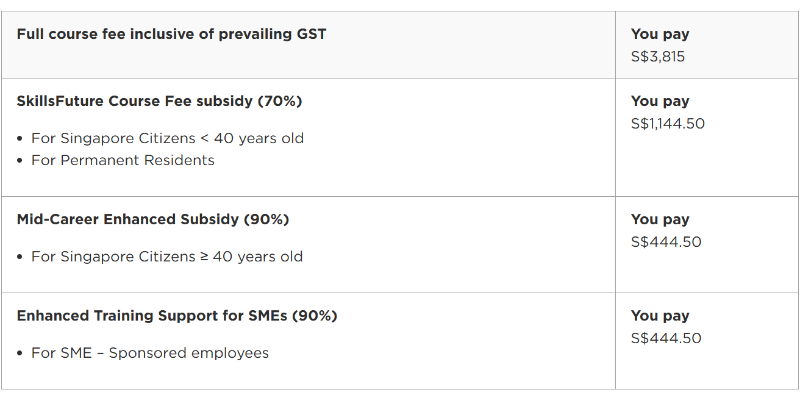
Course fees: $3,815 (Before Funding), $1,144.50 (Singaporean/PR), $444.50 (Singaporean > 40 years old) inclusive of 9% GST.
Skills Covered
PROFICIENCY LEVEL GUIDE
Beginner: Introduce the subject matter without the need to have any prerequisites.
Proficient: Requires learners to have prior knowledge of the subject.
Expert: Involves advanced and more complex understanding of the subject.
- Cybersecurity (Proficiency level: Proficient)
Speakers
Trainer's Profile:
Matthias Yeo, CEO, CyberXCenter Pte Ltd
Matthias is the Co-founder and Chief Executive Officer of CyberXCenter, a Cyber security firm in Singapore. The company specializes in building cybersecurity capabilities for Industrial Control Systems (ICS) by offering services such as training, cyber exercises, and research. He conducts research on vulnerabilities in critical infrastructure, including Operational Technology (OT) and 5G networks, to enhance national security. Matthias is actively involved in national level cyber exercise such as CISS (Critical Infrastructure Security Showdown) and CiDex (Critical Infrastructure Defence Exercise) organized by DoD (Department of Defense). He ran Tabletop Exercise (TTX) and programme planning for United Nation. CyberXCenter has received multiple accolades, including the 2024 Cyber Security Excellence Award
Trainer's Profile:
Jonathan Choo, Researcher, CyberXCenter Pte Ltd
Jonathan Peter Choo is a cybersecurity researcher specializing in Operational Technology (OT) security and 5G infrastructure. He has 1.5 years of hands-on experience deploying and managing on-premise Kubernetes clusters on Proxmox, analyzing 5G traffic with Wireshark, and developing training materials on call flows and PDU session establishment. He has also studied Modbus traffic and built personal labs simulating enterprise and OT environments. Jonathan holds a Specialist Diploma in OT Cybersecurity (Network and System Defence, 2026), ISC² Certified in Cybersecurity, CompTIA Security+, and Security Blue Team Level 1, equipping him to teach practical OT cybersecurity concepts effectively.