×
 
 Back to all courses

[May 2025] Certified Ethical Hacker (CEH)

0%

Overview

The CEH certification training course in Singapore equips professionals with cutting-edge AI-powered tools and techniques to excel in ethical hacking. This advanced course covers every phase of ethical hacking, from reconnaissance and scanning to maintaining access and securing systems. Leveraging AI integration, participants will learn to automate threat detection, predict potential breaches, and swiftly respond to cyber incidents. Additionally, the course focuses on securing AI-driven technologies, empowering organizations to stay resilient against evolving threats.

The CEH certification integrates practical experience and a structured approach to ethical hacking methodologies. By combining ethical hacking expertise with advanced AI capabilities, participants gain the skills needed to conduct proactive threat hunting, anomaly detection, and predictive analysis. This certification not only deepens your understanding of system vulnerabilities but also prepares you to strengthen security measures, reducing the risk of cyber-attacks and ensuring robust organizational defenses.

Course Description & Learning Outcomes

CEH provides the most extensive, immersive hands-on lab and practice range experience in the market, along with a thorough training program designed to prepare you for the certification exam.


What You Will Learn ?

- Leverage AI-driven techniques to enhance your ethical hacking skills, automate threat detection, predict breaches, and stay ahead of evolving cyber threats.

- Key issues plaguing the information security world include ethical hacking, information security controls, laws, and standards.

- Conduct foot printing and reconnaissance utilising cutting-edge techniques and tools as an essential pre-attack phase required in ethical hacking.

- Network scanning countermeasures and techniques.

- Enumeration countermeasures and techniques.

- Conducting vulnerability analysis, which involved identifying security weaknesses within the network, communication infrastructure, and end systems of the target organization.

- Unveiling system and network weaknesses using techniques such as steganalysis attacks, system hacking methodology, covering traced and steganography.

- Social engineering techniques and how to identify theft attacks to audit human- level vulnerabilities and suggest social engineering countermeasures.

- DoS/DDoS tools and attack techniques to audit a target and DoS/DDoS countermeasures.

- Various forms of malware (such as Trojans, viruses, worms, etc.), conducting system audits to detect malware attacks, analysing malware, and implementing countermeasures.

- Countermeasures, session hijacking techniques to uncover session management at network-level, authentication/authorisation, and cryptographic weaknesses.

- Packet sniffing techniques to discover network vulnerabilities and countermeasures to defend sniffing.

- Assessing vulnerabilities in web applications involves utilizing a comprehensive web application hacking methodology to identify web application attacks and implementing appropriate countermeasures.

- Countermeasures, injection detection tools to detect SQL injection attempts, and SQL injection attack techniques.

- Web server attacks and a comprehensive attack methodology to audit vulnerabilities in web server infrastructure, and countermeasures.

- IDS, honeypot and firewall evasion techniques, evasion tools and techniques to audit a network perimeter for weaknesses, and countermeasures.

- Attack vectors on mobile platforms, exploits targeting Android vulnerabilities, and guidelines along with tools for enhancing mobile security.

- Discover potential risks targeting IoT and OT platforms and acquire strategies for securely safeguarding IoT and OT devices.

- Wireless encryption, wireless hacking tools, wireless hacking methodology, and Wi-Fi security tools.

- Penetration testing, security audit, vulnerability assessment, and penetration testing roadmap.

- Public Key Infrastructure (PKI), cryptography ciphers, cryptanalysis tools, and cryptography attacks.

- Cloud computing concepts (Server less computing, container technology), various threats/attacks, and security techniques and tools.


Course Outline

Module 01: Introduction to Ethical Hacking

Module 02: Foot printing and Reconnaissance

Module 03: Scanning Networks

Module 04: Enumeration

Module 05: Vulnerability Analysis

Module 06: System Hacking

Module 07: Malware Threats

Module 08: Sniffing

Module 09: Social Engineering

Module 10: Denial-of-Service

Module 11: Session Hijacking

Module 12: Evading IDS, Firewalls, and Honeypot

Module 13: Hacking Web Servers

Module 14: Hacking Web Applications

Module 15: SQL Injection

Module 17: Hacking Mobile Platforms

Module 18: IoT and OT Hacking

Module 19: Cloud Computing

Module 20: Cryptography

The objective of this funded CEH course is to assist you in becoming a master of ethical hacking methodology that can be used in an ethical hacking or penetration testing situation. Our expert-led, funded programs can elevate your cybersecurity journey. With online flexibility and comprehensive content, become a certified ethical hacker ready for any penetration testing scenario, all through our convenient online training courses.

At the end of this course, you will be prepared for EC-Council Certified Ethical Hacker exam 312-50.

For more information, please click here.

Schedule

Start Date: 26 May 2025, Monday
End Date: 30 Jun 2025, Monday

Duration: 5 Days, 36.25 hours Timing: 9am - 5.15pm

Location: Online

Pricing

Course fees: If you meet the eligibility criteria, course fees can be subsidised by up to 70%. Moreover, SkillsFuture Credit can be applied to cover course fees in addition to existing government subsidies.
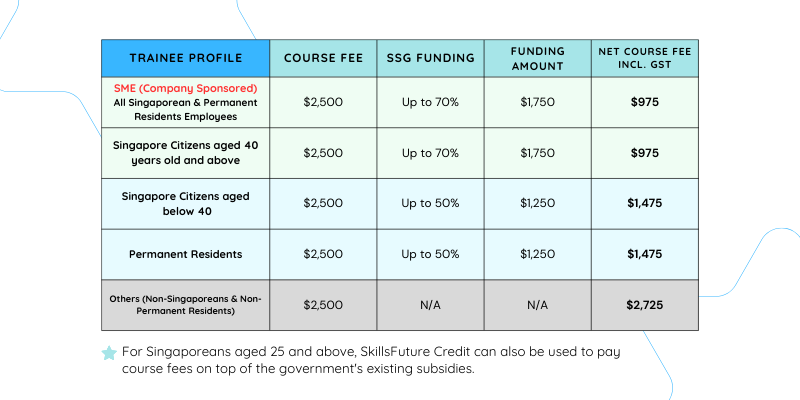
Course Pricing

Skills Covered

PROFICIENCY LEVEL GUIDE
Beginner: Introduce the subject matter without the need to have any prerequisites.
Proficient: Requires learners to have prior knowledge of the subject.
Expert: Involves advanced and more complex understanding of the subject.

  • Cybersecurity (Proficiency level: Proficient)
 Back to all courses

[Apr 2025] CompTIA Security+

0%

Overview

CompTIA Security+ is the pinnacle of cybersecurity, including the most in-demand skills in zero trust, current threats, risk, automation, IoT, and more. Once you are certified, you will grasp the fundamental skills required for career success – and employers will notice.

The CompTIA Security+ examination certifies that you possess the necessary abilities and knowledge to:

- Monitor and protect hybrid environments that include mobile, IoT, cloud, and operational technologies.

- Demonstrate an understanding of applicable policies and regulations, including risk, compliance, and governance concepts.

- Assess the security posture of an enterprise environment and recommend and implement appropriate security solutions.

- Detect, analyse, and respond to security problems and events.

CompTIA Security+ is ISO 17024 compliant and has been authorised by the US Department of Defence to fulfil directive 8140/8570.01-M criteria. ANSI certification is valued by regulators and governments because it instils trust and confidence in the outcomes of an approved programme. Since 1 Jan 2011, over 2.3 million CompTIA ANSI/ISO-accredited examinations have been given.

Course Description & Learning Outcomes

Course Outline

  1. Security Fundamentals

    - Information Security Controls & Cycle

    - Fundamentals of Cryptography

    - Fundamentals of Security Policy

    - Methods of Authentication

  1. Identifying Security Threats and Vulnerabilities

    - Malware

    - Social Engineering

    - Software-Based Threats

    - Network-Based Threats

    - Physical Vulnerabilities and Threats

    - Wireless Vulnerabilities and Threats

  1. Managing Data, Application, and Host Security

    - Manage Data Security

    - Manage Application Security

    - Manage Device and Host Security

    - Manage Mobile Security

  1. Implementing Network Security

    - Configure Security Parameters on Network Devices and Technologies

    - Network Design Components and Elements

    - Secure Wireless Traffic

    - Apply Principles of Secure Network Administration

    - Implement Networking Services and Protocols

  1. Implementing Account Management, Access Control and Authentication

    - Implement Account Management Security Controls

    - Authentication Services and Access Control

  1. Managing Certificates

    - Install a Certificate Authority (CA) Hierarchy

    - Enrol Certificates

    - Secure Network Traffic by Using Certificates

    - Restore and Back Up Certificates and Private Keys

    - Revoke and Renew Certificates

    - Restore Certificates and Private Keys

  2. Implementing Compliance and Operational Security

    - Physical Security

    - Legal Compliance

    - Security Training and Awareness

    - Integrate Systems and Data with Third Parties

  3. Management of Risk

    - Risk Analysis

    - Implement Vulnerability Assessment Tools and Techniques

    - Scan for Vulnerabilities

    - Mitigation and Deterrent Techniques

  4. Managing and Troubleshooting Security Incidents

    - Recover from a Security Incident

    - Respond to Security Incidents

  5. Business Continuity and Disaster Recovery Planning

    - Business Continuity

    - Plan for Disaster Recovery

Threats, Vulnerabilities & Mitigations

This course focuses on responding to common threats, security incidents, vulnerabilities, and cyberattacks, as well as effective mitigation strategies and safeguarding hybrid settings.

Security Architecture

Includes security implications of various architecture models, enterprise infrastructure security concepts, and data protection measures.

General Security Concepts

Includes fundamental cybersecurity concepts and language to lay the groundwork for security controls reviewed throughout the examination.

Security Program Management & Oversight

Updated to better represent the communication and reporting abilities necessary for Security+ job responsibilities in compliance, governance, assessment, security awareness and risk management.

Security Operations

This includes implementing and improving security and vulnerability management approaches, as well as understanding the security implications of proper software, hardware, and data management.

Fo more information, please click here.

Schedule

Start Date: 07 Apr 2025, Monday
End Date: 11 Apr 2025, Friday

Duration: 5 Days, 40 hours Timing: 9am - 6pm

Location: Online

Pricing

Course fees: If you meet the eligibility criteria, course fees can be subsidised by up to 70%. Moreover, SkillsFuture Credit can be applied to cover course fees in addition to existing government subsidies.

Course Pricing

Skills Covered

PROFICIENCY LEVEL GUIDE
Beginner: Introduce the subject matter without the need to have any prerequisites.
Proficient: Requires learners to have prior knowledge of the subject.
Expert: Involves advanced and more complex understanding of the subject.

  • Cybersecurity (Proficiency level: Proficient)
 Back to all courses

[Apr 2025] Certified Information Security Manager (CISM)

0%

Overview

As a working professional based in Singapore, the Certified Information Security Manager (CISM) course offers you a four-day training program packed with intensive learning sessions. Enrolling in this course will enable you to properly acquire the necessary skills and knowledge expected of proficient information security managers.

At the end of this course, you will be excellently prepared for the CISM exam. What's more, regardless of whether you are actively gearing up for the exam or not, obtaining the CISM certification through this training program remains a valuable way for you to equip yourself with insider knowledge of the five core competencies required of all established information security managers.

Course Description & Learning Outcomes

Course Outline

Some of the core topics featured in the CISM course syllabus include:

Introduction

- CISM Certification Prerequisites

- Examination information

- CISM Certification Application

- CISM Certification Maintenance and Renewal

Domain 1 : Information Security Governance

- Introduction and Benefits of Information Security Governance

- Components of Governance Framework

- Roles & Responsibilities

- Information Security Metrics

- Information Security Strategy Frameworks

- Information Security Implementation Program Frameworks

Domain 2 : Information Risk Management and Compliance

- Topics

- Introduction

- Information Asset Classification and Protection

- Roles & Responsibilities

- Introduction to Risk Management

- Risk Management Process

- Risk Identification

- Risk Treatment

- Controls

- Risk Monitoring and Analysis

- HR Risk

- Risk Reporting


Domain 3 : Information Security Programme Development and Management

- Introduction

- Outcomes

- IS Program

- Framework Components

- IS Program Roadmap

- Information Security Infrastructure and Architecture

- Security Program Management Administration

- Services and Operational Activities

- Controls

- Review and Audit

Domain 4 : Information Security Incident Management

- Introduction

- Objectives

- Incident Management Procedures

- Developing Incident Response Plan

- Roles and Responsibilities

- Content of the Incident Response Plan

- Disaster Recovery Procedures and Business Continuity


Examination Preparation and Techniques

- Administration

- Techniques

- Tips and Hints

- FAQ

For more information, please click here

Schedule

Start Date: 07 Apr 2025, Monday
End Date: 10 Apr 2025, Thursday

Duration: 4 Days, 30 hours Timing: 9am - 5.30pm Location: Virtual

Location: Online

Pricing

Course fees: If you meet the eligibility criteria, course fees can be subsidised by up to 70%. Moreover, SkillsFuture Credit can be applied to cover course fees in addition to existing government subsidies.

Course Pricing

Skills Covered

PROFICIENCY LEVEL GUIDE
Beginner: Introduce the subject matter without the need to have any prerequisites.
Proficient: Requires learners to have prior knowledge of the subject.
Expert: Involves advanced and more complex understanding of the subject.

  • Cybersecurity (Proficiency level: Expert)
 Back to all courses

[Mar 2025] Certified Ethical Hacker (CEH)

0%

Overview

The CEH certification training course in Singapore equips professionals with cutting-edge AI-powered tools and techniques to excel in ethical hacking. This advanced course covers every phase of ethical hacking, from reconnaissance and scanning to maintaining access and securing systems. Leveraging AI integration, participants will learn to automate threat detection, predict potential breaches, and swiftly respond to cyber incidents. Additionally, the course focuses on securing AI-driven technologies, empowering organizations to stay resilient against evolving threats.

The CEH certification integrates practical experience and a structured approach to ethical hacking methodologies. By combining ethical hacking expertise with advanced AI capabilities, participants gain the skills needed to conduct proactive threat hunting, anomaly detection, and predictive analysis. This certification not only deepens your understanding of system vulnerabilities but also prepares you to strengthen security measures, reducing the risk of cyber-attacks and ensuring robust organizational defenses.

Course Description & Learning Outcomes

CEH provides the most extensive, immersive hands-on lab and practice range experience in the market, along with a thorough training program designed to prepare you for the certification exam.


What You Will Learn ?

- Leverage AI-driven techniques to enhance your ethical hacking skills, automate threat detection, predict breaches, and stay ahead of evolving cyber threats.

- Key issues plaguing the information security world include ethical hacking, information security controls, laws, and standards.

- Conduct foot printing and reconnaissance utilising cutting-edge techniques and tools as an essential pre-attack phase required in ethical hacking.

- Network scanning countermeasures and techniques.

- Enumeration countermeasures and techniques.

- Conducting vulnerability analysis, which involved identifying security weaknesses within the network, communication infrastructure, and end systems of the target organization.

- Unveiling system and network weaknesses using techniques such as steganalysis attacks, system hacking methodology, covering traced and steganography.

- Social engineering techniques and how to identify theft attacks to audit human- level vulnerabilities and suggest social engineering countermeasures.

- DoS/DDoS tools and attack techniques to audit a target and DoS/DDoS countermeasures.

- Various forms of malware (such as Trojans, viruses, worms, etc.), conducting system audits to detect malware attacks, analysing malware, and implementing countermeasures.

- Countermeasures, session hijacking techniques to uncover session management at network-level, authentication/authorisation, and cryptographic weaknesses.

- Packet sniffing techniques to discover network vulnerabilities and countermeasures to defend sniffing.

- Assessing vulnerabilities in web applications involves utilizing a comprehensive web application hacking methodology to identify web application attacks and implementing appropriate countermeasures.

- Countermeasures, injection detection tools to detect SQL injection attempts, and SQL injection attack techniques.

- Web server attacks and a comprehensive attack methodology to audit vulnerabilities in web server infrastructure, and countermeasures.

- IDS, honeypot and firewall evasion techniques, evasion tools and techniques to audit a network perimeter for weaknesses, and countermeasures.

- Attack vectors on mobile platforms, exploits targeting Android vulnerabilities, and guidelines along with tools for enhancing mobile security.

- Discover potential risks targeting IoT and OT platforms and acquire strategies for securely safeguarding IoT and OT devices.

- Wireless encryption, wireless hacking tools, wireless hacking methodology, and Wi-Fi security tools.

- Penetration testing, security audit, vulnerability assessment, and penetration testing roadmap.

- Public Key Infrastructure (PKI), cryptography ciphers, cryptanalysis tools, and cryptography attacks.

- Cloud computing concepts (Server less computing, container technology), various threats/attacks, and security techniques and tools.


Course Outline

Module 01: Introduction to Ethical Hacking

Module 02: Foot printing and Reconnaissance

Module 03: Scanning Networks

Module 04: Enumeration

Module 05: Vulnerability Analysis

Module 06: System Hacking

Module 07: Malware Threats

Module 08: Sniffing

Module 09: Social Engineering

Module 10: Denial-of-Service

Module 11: Session Hijacking

Module 12: Evading IDS, Firewalls, and Honeypot

Module 13: Hacking Web Servers

Module 14: Hacking Web Applications

Module 15: SQL Injection

Module 17: Hacking Mobile Platforms

Module 18: IoT and OT Hacking

Module 19: Cloud Computing

Module 20: Cryptography

The objective of this funded CEH course is to assist you in becoming a master of ethical hacking methodology that can be used in an ethical hacking or penetration testing situation. Our expert-led, funded programs can elevate your cybersecurity journey. With online flexibility and comprehensive content, become a certified ethical hacker ready for any penetration testing scenario, all through our convenient online training courses.

At the end of this course, you will be prepared for EC-Council Certified Ethical Hacker exam 312-50.

For more information, please click here.

Schedule

Start Date: 24 Mar 2025, Monday
End Date: 28 Mar 2025, Friday

Duration: 5 Days, 36.25 hours Timing: 9am - 5.15pm

Location: 3 Kallang Jct, #04-02 Vanguard Campus, Singapore 339265, 339265

Pricing

Course fees: If you meet the eligibility criteria, course fees can be subsidised by up to 70%. Moreover, SkillsFuture Credit can be applied to cover course fees in addition to existing government subsidies.

Course Pricing

Skills Covered

PROFICIENCY LEVEL GUIDE
Beginner: Introduce the subject matter without the need to have any prerequisites.
Proficient: Requires learners to have prior knowledge of the subject.
Expert: Involves advanced and more complex understanding of the subject.

  • Cybersecurity (Proficiency level: Proficient)
 Back to all courses

[Feb 2025] Certified Information Security Manager (CISM)

0%

Overview

As a working professional based in Singapore, the Certified Information Security Manager (CISM) course offers you a four-day training program packed with intensive learning sessions. Enrolling in this course will enable you to properly acquire the necessary skills and knowledge expected of proficient information security managers.

At the end of this course, you will be excellently prepared for the CISM exam. What's more, regardless of whether you are actively gearing up for the exam or not, obtaining the CISM certification through this training program remains a valuable way for you to equip yourself with insider knowledge of the five core competencies required of all established information security managers.

Course Description & Learning Outcomes

Course Outline

Some of the core topics featured in the CISM course syllabus include:

Introduction

- CISM Certification Prerequisites

- Examination information

- CISM Certification Application

- CISM Certification Maintenance and Renewal

Domain 1 : Information Security Governance

- Introduction and Benefits of Information Security Governance

- Components of Governance Framework

- Roles & Responsibilities

- Information Security Metrics

- Information Security Strategy Frameworks

- Information Security Implementation Program Frameworks

Domain 2 : Information Risk Management and Compliance

- Topics

- Introduction

- Information Asset Classification and Protection

- Roles & Responsibilities

- Introduction to Risk Management

- Risk Management Process

- Risk Identification

- Risk Treatment

- Controls

- Risk Monitoring and Analysis

- HR Risk

- Risk Reporting


Domain 3 : Information Security Programme Development and Management

- Introduction

- Outcomes

- IS Program

- Framework Components

- IS Program Roadmap

- Information Security Infrastructure and Architecture

- Security Program Management Administration

- Services and Operational Activities

- Controls

- Review and Audit

Domain 4 : Information Security Incident Management

- Introduction

- Objectives

- Incident Management Procedures

- Developing Incident Response Plan

- Roles and Responsibilities

- Content of the Incident Response Plan

- Disaster Recovery Procedures and Business Continuity


Examination Preparation and Techniques

- Administration

- Techniques

- Tips and Hints

- FAQ

For more information, please click here

Schedule

Start Date: 03 Feb 2025, Monday
End Date: 06 Feb 2025, Thursday

Duration: 4 Days, 30 hours Timing: 9am - 5.30pm Location: Virtual

Location: 3 Kallang Jct, #04-02 Vanguard Campus, Singapore 339265, 339265

Pricing

Course fees: If you meet the eligibility criteria, course fees can be subsidised by up to 70%. Moreover, SkillsFuture Credit can be applied to cover course fees in addition to existing government subsidies.

Course Pricing

Skills Covered

PROFICIENCY LEVEL GUIDE
Beginner: Introduce the subject matter without the need to have any prerequisites.
Proficient: Requires learners to have prior knowledge of the subject.
Expert: Involves advanced and more complex understanding of the subject.

  • Cybersecurity (Proficiency level: Expert)
 Back to all courses

[Feb 2025] CompTIA Security+

0%

Overview

CompTIA Security+ is the pinnacle of cybersecurity, including the most in-demand skills in zero trust, current threats, risk, automation, IoT, and more. Once you are certified, you will grasp the fundamental skills required for career success – and employers will notice.

The CompTIA Security+ examination certifies that you possess the necessary abilities and knowledge to:

- Monitor and protect hybrid environments that include mobile, IoT, cloud, and operational technologies.

- Demonstrate an understanding of applicable policies and regulations, including risk, compliance, and governance concepts.

- Assess the security posture of an enterprise environment and recommend and implement appropriate security solutions.

- Detect, analyse, and respond to security problems and events.

CompTIA Security+ is ISO 17024 compliant and has been authorised by the US Department of Defence to fulfil directive 8140/8570.01-M criteria. ANSI certification is valued by regulators and governments because it instils trust and confidence in the outcomes of an approved programme. Since 1 Jan 2011, over 2.3 million CompTIA ANSI/ISO-accredited examinations have been given.

Course Description & Learning Outcomes

Course Outline

  1. Security Fundamentals

    - Information Security Controls & Cycle

    - Fundamentals of Cryptography

    - Fundamentals of Security Policy

    - Methods of Authentication

  1. Identifying Security Threats and Vulnerabilities

    - Malware

    - Social Engineering

    - Software-Based Threats

    - Network-Based Threats

    - Physical Vulnerabilities and Threats

    - Wireless Vulnerabilities and Threats

  1. Managing Data, Application, and Host Security

    - Manage Data Security

    - Manage Application Security

    - Manage Device and Host Security

    - Manage Mobile Security

  1. Implementing Network Security

    - Configure Security Parameters on Network Devices and Technologies

    - Network Design Components and Elements

    - Secure Wireless Traffic

    - Apply Principles of Secure Network Administration

    - Implement Networking Services and Protocols

  1. Implementing Account Management, Access Control and Authentication

    - Implement Account Management Security Controls

    - Authentication Services and Access Control

  1. Managing Certificates

    - Install a Certificate Authority (CA) Hierarchy

    - Enrol Certificates

    - Secure Network Traffic by Using Certificates

    - Restore and Back Up Certificates and Private Keys

    - Revoke and Renew Certificates

    - Restore Certificates and Private Keys

  2. Implementing Compliance and Operational Security

    - Physical Security

    - Legal Compliance

    - Security Training and Awareness

    - Integrate Systems and Data with Third Parties

  3. Management of Risk

    - Risk Analysis

    - Implement Vulnerability Assessment Tools and Techniques

    - Scan for Vulnerabilities

    - Mitigation and Deterrent Techniques

  4. Managing and Troubleshooting Security Incidents

    - Recover from a Security Incident

    - Respond to Security Incidents

  5. Business Continuity and Disaster Recovery Planning

    - Business Continuity

    - Plan for Disaster Recovery

Threats, Vulnerabilities & Mitigations

This course focuses on responding to common threats, security incidents, vulnerabilities, and cyberattacks, as well as effective mitigation strategies and safeguarding hybrid settings.

Security Architecture

Includes security implications of various architecture models, enterprise infrastructure security concepts, and data protection measures.

General Security Concepts

Includes fundamental cybersecurity concepts and language to lay the groundwork for security controls reviewed throughout the examination.

Security Program Management & Oversight

Updated to better represent the communication and reporting abilities necessary for Security+ job responsibilities in compliance, governance, assessment, security awareness and risk management.

Security Operations

This includes implementing and improving security and vulnerability management approaches, as well as understanding the security implications of proper software, hardware, and data management.

Fo more information, please click here.

Schedule

Start Date: 03 Feb 2025, Monday
End Date: 07 Feb 2025, Friday

Duration: 5 Days, 40 hours Timing: 9am - 6pm

Location: Online

Pricing

Course fees: If you meet the eligibility criteria, course fees can be subsidised by up to 70%. Moreover, SkillsFuture Credit can be applied to cover course fees in addition to existing government subsidies.

Course Pricing

Skills Covered

PROFICIENCY LEVEL GUIDE
Beginner: Introduce the subject matter without the need to have any prerequisites.
Proficient: Requires learners to have prior knowledge of the subject.
Expert: Involves advanced and more complex understanding of the subject.

  • Cybersecurity (Proficiency level: Proficient)
 Back to all courses

[Nov 2025] Certified Information Systems Auditor (CISA)

0%

Overview

Embark on a transformative journey with our comprehensive CISA course, meticulously designed to equip you with the knowledge and skills needed to conquer the ISACA CRISC Exam. Our mission is clear: to ensure your readiness for CISA certification and empower you to effectively manage the risks faced by your organization. Enrol now to enhance your skills and advance your career through this comprehensive CISA course in Singapore.

The course is prepared and delivered based on content from the ISACA CISA (Certified Information Systems Auditor) Review Manual 27th edition, making it an excellent resource for anyone who is seeking CISA certification in Singapore. The course covers five (5) domains, including Information System Auditing Process; Management and Governance of IT; Information Systems Acquisition, Implementation, and Development; Information Systems Operation; and Business Resilience and Protection of Information Assets.

For more information, please click here.

Course Description & Learning Outcomes

The CISA course is conducted over four days, and the content is organised into five domains. Topics covered in each of the domains are as shown below:

Domain 1: Information System Auditing Process

  • Planning

    - IS Audit Standards, Guidelines, and Codes of Ethics

    - Types of Controls

    - Types of Audits and Assessments

    - Risk-Based Audit Planning

    - Business Processes

  • Execution

    - Data Analytics

    - Quality Assurance and Improvement of the Audit Process

    - Sampling Methodology

    - Audit Evidence Collection Techniques

    - Audit Project Management

    - Reporting and Communication and Reporting Techniques


Domain 2: Governance and Management of IT 

  •  IT Governance

    - IT Strategy and IT Governance

    - IT-Related Frameworks

    - IT Policies, Procedures and Standards

    - Organisational Structure

    - Enterprise Architecture

    - Enterprise Risk Management

    - Maturity Models

    - Organisation Affecting Laws, Regulations, and Industry Standards

  • IT Management

    - IT Resource Management

    - IT Service Provider Management and Acquisition

    - IT Performance Monitoring and Reporting

    - Quality Assurance and Quality Management of IT

Domain 3: Information Systems Acquisition, Development and implementation 

  • Quality Assurance and Quality Management of IT

    - Project Management and Governance

    - Feasibility Analysis and Business Case

    - System Development Methodologies

    - Control Identification and Design

  • Implementation of Information Systems

    - Testing Methodologies

    - Configuration and Release Management

    - System Migration, Infrastructure Deployment, and Data Conversion

    - Post-implementation Review

Domain 4: Business Resilience and Information Systems Operation

  • Information Systems Operations

    - Common Technology Components

    - IT Asset Management

    - Production Process Automation and Job Scheduling

    - System Interfaces

    - End-User Computing

    - Data Governance

    - Systems Performance Management

    - Problem and Incident Management

    - Configuration, Change, Release, and Patch Management

    - IT Service Level Management

    - Database Management

  •  Business Resilience

    - Business Impact Analysis (BIA)

    - System Resiliency

    - Data Backup, Storage, and Restoration

    - Business Continuity Plan (BCP)

    - Disaster Recovery Plans (DRP)

Domain 5: Protection of Information Assets 

  • Information Asset Security and Control

    - Information Asset Security Frameworks, Standards, and Guidelines

    - Privacy Principles

    - Environmental Controls and Physical Access

    - Identity and Access Management

    - Network and End-Point Security

    - Data Classification

    - Data Encryption and Encryption-Related Techniques

    - Public Key Infrastructure (PKI)

    - Web-Based Communication Techniques

    - Virtualised Environments

    - Wireless, Mobile, and Internet-of-Things (IoT) Devices

  •  Security Event Management

    - Security Awareness Programs and Trainings

    - Information System Attack Techniques and Methods

    - Security Testing Techniques and Tools

    - Security Monitoring Techniques and Tools

    - Incident Response Management

    - Forensics and Evidence Collection

At the end of this course you will:

- Understand the methodology, phases and activities required to plan, assess risk, conduct an audit and communicate the audit progress, findings and recommendations, including relevant considerations for CISA certification in Singapore.

- Understand the methodology and activities required for IT Strategy Alignment, IT Organisational structure, Implementation and Management of T policies and policies and Practices Compliance to regulatory and legislation requirements and knowledge to evaluate their effectiveness.

- Understand the definitions, methodology and activities required for systems development life cycle, systems implementation and knowledge required to evaluate their effectiveness.

- Understand the definitions, methodology and phases involved in Business continuity, IT Service Operations.

- Understand the components of Physical Security, Logical Access Security, data classification, data life cycle, Security Controls, Threat and Vulnerability Assessment, Security Testing, Security Operations, Security Incident Process, and evaluate their effectiveness, aligning with the principles covered in a CISA course.

Schedule

Start Date: 03 Nov 2025, Monday
End Date: 06 Nov 2025, Thursday

Duration: 4 Days, 32.5 hours Timing: 9am - 6pm

Location: Online

Pricing

Course fees: If you meet the eligibility criteria, course fees can be subsidised by up to 70%. Moreover, SkillsFuture Credit can be applied to cover course fees in addition to existing government subsidies.

Course Pricing

Skills Covered

PROFICIENCY LEVEL GUIDE
Beginner: Introduce the subject matter without the need to have any prerequisites.
Proficient: Requires learners to have prior knowledge of the subject.
Expert: Involves advanced and more complex understanding of the subject.

  • Cybersecurity (Proficiency level: Expert)
 Back to all courses

[Sep 2025] Certified Information Systems Auditor (CISA)

0%

Overview

Embark on a transformative journey with our comprehensive CISA course, meticulously designed to equip you with the knowledge and skills needed to conquer the ISACA CRISC Exam. Our mission is clear: to ensure your readiness for CISA certification and empower you to effectively manage the risks faced by your organization. Enrol now to enhance your skills and advance your career through this comprehensive CISA course in Singapore.

The course is prepared and delivered based on content from the ISACA CISA (Certified Information Systems Auditor) Review Manual 27th edition, making it an excellent resource for anyone who is seeking CISA certification in Singapore. The course covers five (5) domains, including Information System Auditing Process; Management and Governance of IT; Information Systems Acquisition, Implementation, and Development; Information Systems Operation; and Business Resilience and Protection of Information Assets.

For more information, please click here.

Course Description & Learning Outcomes

The CISA course is conducted over four days, and the content is organised into five domains. Topics covered in each of the domains are as shown below:

Domain 1: Information System Auditing Process

  • Planning

    - IS Audit Standards, Guidelines, and Codes of Ethics

    - Types of Controls

    - Types of Audits and Assessments

    - Risk-Based Audit Planning

    - Business Processes

  • Execution

    - Data Analytics

    - Quality Assurance and Improvement of the Audit Process

    - Sampling Methodology

    - Audit Evidence Collection Techniques

    - Audit Project Management

    - Reporting and Communication and Reporting Techniques


Domain 2: Governance and Management of IT 

  •  IT Governance

    - IT Strategy and IT Governance

    - IT-Related Frameworks

    - IT Policies, Procedures and Standards

    - Organisational Structure

    - Enterprise Architecture

    - Enterprise Risk Management

    - Maturity Models

    - Organisation Affecting Laws, Regulations, and Industry Standards

  • IT Management

    - IT Resource Management

    - IT Service Provider Management and Acquisition

    - IT Performance Monitoring and Reporting

    - Quality Assurance and Quality Management of IT

Domain 3: Information Systems Acquisition, Development and implementation 

  • Quality Assurance and Quality Management of IT

    - Project Management and Governance

    - Feasibility Analysis and Business Case

    - System Development Methodologies

    - Control Identification and Design

  • Implementation of Information Systems

    - Testing Methodologies

    - Configuration and Release Management

    - System Migration, Infrastructure Deployment, and Data Conversion

    - Post-implementation Review

Domain 4: Business Resilience and Information Systems Operation

  • Information Systems Operations

    - Common Technology Components

    - IT Asset Management

    - Production Process Automation and Job Scheduling

    - System Interfaces

    - End-User Computing

    - Data Governance

    - Systems Performance Management

    - Problem and Incident Management

    - Configuration, Change, Release, and Patch Management

    - IT Service Level Management

    - Database Management

  •  Business Resilience

    - Business Impact Analysis (BIA)

    - System Resiliency

    - Data Backup, Storage, and Restoration

    - Business Continuity Plan (BCP)

    - Disaster Recovery Plans (DRP)

Domain 5: Protection of Information Assets 

  • Information Asset Security and Control

    - Information Asset Security Frameworks, Standards, and Guidelines

    - Privacy Principles

    - Environmental Controls and Physical Access

    - Identity and Access Management

    - Network and End-Point Security

    - Data Classification

    - Data Encryption and Encryption-Related Techniques

    - Public Key Infrastructure (PKI)

    - Web-Based Communication Techniques

    - Virtualised Environments

    - Wireless, Mobile, and Internet-of-Things (IoT) Devices

  •  Security Event Management

    - Security Awareness Programs and Trainings

    - Information System Attack Techniques and Methods

    - Security Testing Techniques and Tools

    - Security Monitoring Techniques and Tools

    - Incident Response Management

    - Forensics and Evidence Collection

At the end of this course you will:

- Understand the methodology, phases and activities required to plan, assess risk, conduct an audit and communicate the audit progress, findings and recommendations, including relevant considerations for CISA certification in Singapore.

- Understand the methodology and activities required for IT Strategy Alignment, IT Organisational structure, Implementation and Management of T policies and policies and Practices Compliance to regulatory and legislation requirements and knowledge to evaluate their effectiveness.

- Understand the definitions, methodology and activities required for systems development life cycle, systems implementation and knowledge required to evaluate their effectiveness.

- Understand the definitions, methodology and phases involved in Business continuity, IT Service Operations.

- Understand the components of Physical Security, Logical Access Security, data classification, data life cycle, Security Controls, Threat and Vulnerability Assessment, Security Testing, Security Operations, Security Incident Process, and evaluate their effectiveness, aligning with the principles covered in a CISA course.

Schedule

Start Date: 01 Sep 2025, Monday
End Date: 04 Sep 2025, Thursday

Duration: 4 Days, 32.5 hours Timing: 9am - 6pm

Location: 3 Kallang Jct, #04-02 Vanguard Campus, Singapore 339265, 339265

Pricing

Course fees: If you meet the eligibility criteria, course fees can be subsidised by up to 70%. Moreover, SkillsFuture Credit can be applied to cover course fees in addition to existing government subsidies.

Course Pricing

Skills Covered

PROFICIENCY LEVEL GUIDE
Beginner: Introduce the subject matter without the need to have any prerequisites.
Proficient: Requires learners to have prior knowledge of the subject.
Expert: Involves advanced and more complex understanding of the subject.

  • Cybersecurity (Proficiency level: Expert)
 Back to all courses

[Jun 2025] Certified Information Systems Auditor (CISA)

0%

Overview

Embark on a transformative journey with our comprehensive CISA course, meticulously designed to equip you with the knowledge and skills needed to conquer the ISACA CRISC Exam. Our mission is clear: to ensure your readiness for CISA certification and empower you to effectively manage the risks faced by your organization. Enrol now to enhance your skills and advance your career through this comprehensive CISA course in Singapore.

The course is prepared and delivered based on content from the ISACA CISA (Certified Information Systems Auditor) Review Manual 27th edition, making it an excellent resource for anyone who is seeking CISA certification in Singapore. The course covers five (5) domains, including Information System Auditing Process; Management and Governance of IT; Information Systems Acquisition, Implementation, and Development; Information Systems Operation; and Business Resilience and Protection of Information Assets.

For more information, please click here.

Course Description & Learning Outcomes

The CISA course is conducted over four days, and the content is organised into five domains. Topics covered in each of the domains are as shown below:

Domain 1: Information System Auditing Process

  • Planning

    - IS Audit Standards, Guidelines, and Codes of Ethics

    - Types of Controls

    - Types of Audits and Assessments

    - Risk-Based Audit Planning

    - Business Processes

  • Execution

    - Data Analytics

    - Quality Assurance and Improvement of the Audit Process

    - Sampling Methodology

    - Audit Evidence Collection Techniques

    - Audit Project Management

    - Reporting and Communication and Reporting Techniques


Domain 2: Governance and Management of IT 

  •  IT Governance

    - IT Strategy and IT Governance

    - IT-Related Frameworks

    - IT Policies, Procedures and Standards

    - Organisational Structure

    - Enterprise Architecture

    - Enterprise Risk Management

    - Maturity Models

    - Organisation Affecting Laws, Regulations, and Industry Standards

  • IT Management

    - IT Resource Management

    - IT Service Provider Management and Acquisition

    - IT Performance Monitoring and Reporting

    - Quality Assurance and Quality Management of IT

Domain 3: Information Systems Acquisition, Development and implementation 

  • Quality Assurance and Quality Management of IT

    - Project Management and Governance

    - Feasibility Analysis and Business Case

    - System Development Methodologies

    - Control Identification and Design

  • Implementation of Information Systems

    - Testing Methodologies

    - Configuration and Release Management

    - System Migration, Infrastructure Deployment, and Data Conversion

    - Post-implementation Review

Domain 4: Business Resilience and Information Systems Operation

  • Information Systems Operations

    - Common Technology Components

    - IT Asset Management

    - Production Process Automation and Job Scheduling

    - System Interfaces

    - End-User Computing

    - Data Governance

    - Systems Performance Management

    - Problem and Incident Management

    - Configuration, Change, Release, and Patch Management

    - IT Service Level Management

    - Database Management

  •  Business Resilience

    - Business Impact Analysis (BIA)

    - System Resiliency

    - Data Backup, Storage, and Restoration

    - Business Continuity Plan (BCP)

    - Disaster Recovery Plans (DRP)

Domain 5: Protection of Information Assets 

  • Information Asset Security and Control

    - Information Asset Security Frameworks, Standards, and Guidelines

    - Privacy Principles

    - Environmental Controls and Physical Access

    - Identity and Access Management

    - Network and End-Point Security

    - Data Classification

    - Data Encryption and Encryption-Related Techniques

    - Public Key Infrastructure (PKI)

    - Web-Based Communication Techniques

    - Virtualised Environments

    - Wireless, Mobile, and Internet-of-Things (IoT) Devices

  •  Security Event Management

    - Security Awareness Programs and Trainings

    - Information System Attack Techniques and Methods

    - Security Testing Techniques and Tools

    - Security Monitoring Techniques and Tools

    - Incident Response Management

    - Forensics and Evidence Collection

At the end of this course you will:

- Understand the methodology, phases and activities required to plan, assess risk, conduct an audit and communicate the audit progress, findings and recommendations, including relevant considerations for CISA certification in Singapore.

- Understand the methodology and activities required for IT Strategy Alignment, IT Organisational structure, Implementation and Management of T policies and policies and Practices Compliance to regulatory and legislation requirements and knowledge to evaluate their effectiveness.

- Understand the definitions, methodology and activities required for systems development life cycle, systems implementation and knowledge required to evaluate their effectiveness.

- Understand the definitions, methodology and phases involved in Business continuity, IT Service Operations.

- Understand the components of Physical Security, Logical Access Security, data classification, data life cycle, Security Controls, Threat and Vulnerability Assessment, Security Testing, Security Operations, Security Incident Process, and evaluate their effectiveness, aligning with the principles covered in a CISA course.

Schedule

Start Date: 30 Jun 2025, Monday
End Date: 03 Jul 2025, Thursday

Duration: 4 Days, 32.5 hours Timing: 9am - 6pm

Location: Online

Pricing

Course fees: If you meet the eligibility criteria, course fees can be subsidised by up to 70%. Moreover, SkillsFuture Credit can be applied to cover course fees in addition to existing government subsidies.

Course Pricing

Skills Covered

PROFICIENCY LEVEL GUIDE
Beginner: Introduce the subject matter without the need to have any prerequisites.
Proficient: Requires learners to have prior knowledge of the subject.
Expert: Involves advanced and more complex understanding of the subject.

  • Cybersecurity (Proficiency level: Expert)
 Back to all courses

[Jun 2025] Information Systems Security Professional (CISSP)

0%

Overview

If you are seeking to establish yourself as a reputable information security professional, the Certified Information Systems Security Professional (CISSP) certification is widely recognised in Singapore and internationally. Engaging in CISSP online training can validate your managerial and technical expertise, demonstrating your capability to effectively engineer, design, and oversee an organisation's security framework. The CISSP Common Body of Knowledge (CBK) covers a comprehensive range of topics, ensuring its relevance and applicability across various domains within the information security field.

At the end of this course, you will be able to gain comprehensive and up-to-date knowledge that aligns with the certification requirements of (ISC)² (International Information System Security Certification Consortium, Inc.), renowned as the gold standard for security professionals. This certification is essential for a career in security-related roles, equipping you with the skills necessary to safeguard your organization against sophisticated cyber-attacks. You will also develop a solid background in security concerns, communications, infrastructure, basic cryptography, and operations, along with hands-on experience to effectively design, implement, and manage a security program.

Course Description & Learning Outcomes

Course Outline

The 5-day course heavily focuses on the eight fundamental domains of Information Security.

Domain 1: Risk and Security Management

1.1 Understand and apply concepts of integrity, confidentiality and availability

1.2 Assess and apply security governance principles

1.3 Establish compliance requirements

1.4 Understand regulatory and legal issues that concern information security in a global context

1.5 Understand, promote, and adhere to professional ethics

1.6 Develop, document, and implement security policy, procedures, standards and guidelines

1.7 Analyse, identify and prioritise Business Continuity (BC) requirements

1.8 Enforce and contribute to personnel security guidelines and procedures

1.9 Apply and understand risk management concepts

1.10 Apply and understand threat modelling methodologies and concepts

1.11 Implement risk-based management concepts in the supply chain

1.12 Maintain and establish a security education, awareness and training program

Domain 2: Asset Security

2.1 Identify and classify assets and information

2.2 Determine and maintain asset ownership and information

2.3 Protect privacy

2.4 Ensure proper asset retention

2.5 Determine data security controls

2.6 Establish information and asset handling requirements

Domain 3: Security Architecture and Engineering

3.1 Manage and Implement engineering processes using secure design principles

3.2 Recognise the basic concepts of security models

3.3 Select controls based on systems security requirements

3.4 Recognise security capabilities of information systems (e.g., encryption/decryption, memory protection, Trusted Platform Module (TPM),

3.5 Mitigate and assess the vulnerabilities of security architectures, solution elements and designs

3.6 Mitigate and assess weaknesses in web-based systems

3.7 Mitigate and assess weaknesses in mobile systems

3.8 Mitigate and assess weaknesses in embedded devices

3.9 Apply cryptography

3.10 Apply security principles to facility and site design

3.11 Implement facility and site security controls

Domain 4: Communication and Network Security

4.1 Apply secure design concepts in network architectures

4.2 Secure network components

4.3 Apply secure communication channels according to design

Domain 5: Identity and Access Management (IAM)

5.1 Control logical and physical access to assets

5.2 Manage authentication and identification of people, devices, and service

5.3 Integrate identity as a third-party service

5.4 Manage and implement authorisation mechanisms

5.5 Manage the identity and access provisioning lifecycle

Domain 6: Security Assessment and Testing

6.1 Design and verify tests, assessments and audit strategies

6.2 Manage security control testing

6.3 Manage security process data (e.g., technical and administrative)

6.4 Examine test output and generate a report

6.5 Manage or facilitate security audits

Domain 7: Security Operations

7.1 Support and understand investigations

7.2 Understand requirements for investigation types

7.3 Conduct monitoring and logging activities

7.4 Securely provisioning resources

7.5 Apply and understand foundational security operations concepts

7.6 Apply resource protection techniques

7.7 Conduct incident management

7.8 Maintain and operate detective and preventive measures

7.9 Support and implement patch and vulnerability management

7.10 Understand and Engage in change management processes

7.11 Apply recovery strategies

7.12 Apply Disaster Recovery (DR) processes

7.13 Test Disaster Recovery Plans (DRP)

7.14 Participate in Business Continuity (BC) exercises and planning

7.15 Manage and implement physical security

7.16 Address security concerns and personnel safety

Domain 8: Software Development Security

8.1 Understand and incorporate security in the Software Development Life Cycle (SDLC)

8.2 Recognise and apply security controls in development environments

8.3 Evaluate the benefits of software security

8.4 Evaluate the security impact of acquired software

8.5 Define and implement secure coding standards and guidelines

For more information, please click here.

Schedule

Start Date: 02 Jun 2025, Monday
End Date: 06 Jun 2025, Friday

Duration: 5 Days, 35 hours Timing: 9am - 5pm Location: Virtual

Location: Online

Pricing

Course fees: If you meet the eligibility criteria, course fees can be subsidised by up to 70%. Moreover, SkillsFuture Credit can be applied to cover course fees in addition to existing government subsidies.

Course Pricing

Skills Covered

PROFICIENCY LEVEL GUIDE
Beginner: Introduce the subject matter without the need to have any prerequisites.
Proficient: Requires learners to have prior knowledge of the subject.
Expert: Involves advanced and more complex understanding of the subject.

  • Software Development (Proficiency level: Expert)
  • Cybersecurity (Proficiency level: Expert)

Be part of Singapore's fastest growing Deep Tech Community

Receive the latest updates on ecosystem events and programmes!